
The Tap Test: How an Unpatched Bug and a Silent Suspect Exposed America's Water Grid
An Aure Free Press Deep Dive
Something has changed in how America's water gets to the tap — and it isn't the water.
Between July 26 and July 31, 2026, cyberattackers breached water and wastewater systems across at least seven U.S. states. In Minnesota, more than thirty municipal systems were hit. In Michigan, nine more. Utility operators, unable to trust their own digital controls, reverted to manual operation — turning valves and reading gauges by hand, the way it was done before computers ran the water supply at all.
No ransom note arrived. No demand followed. For a cybersecurity community accustomed to extortion as the default motive, that absence was the loudest signal in the whole incident: this wasn't about money.
Federal investigators are looking at Iran. They have not said so for certain — and that hesitation is not bureaucratic caution so much as an admission of how hard attribution has become in an era of contractors-for-hire, false flags, and copycat tradecraft.
What they can say is this: the pattern matches. It matches a warning about Iranian-affiliated actors exploiting programmable logic controllers — the industrial-grade computers that manage pressure, chemical dosing, and flow at treatment plants nationwide. It matches an update to that warning, issued just days before the attacks began, expanding the list of vulnerable equipment manufacturers. And it matches a vulnerability that has sat unpatched, publicly known, and actively exploited since March.
This is the story of that vulnerability, that warning, and the growing distance between what U.S. security agencies are saying about the threat and what the president is telling the country.
I. Five Days in July
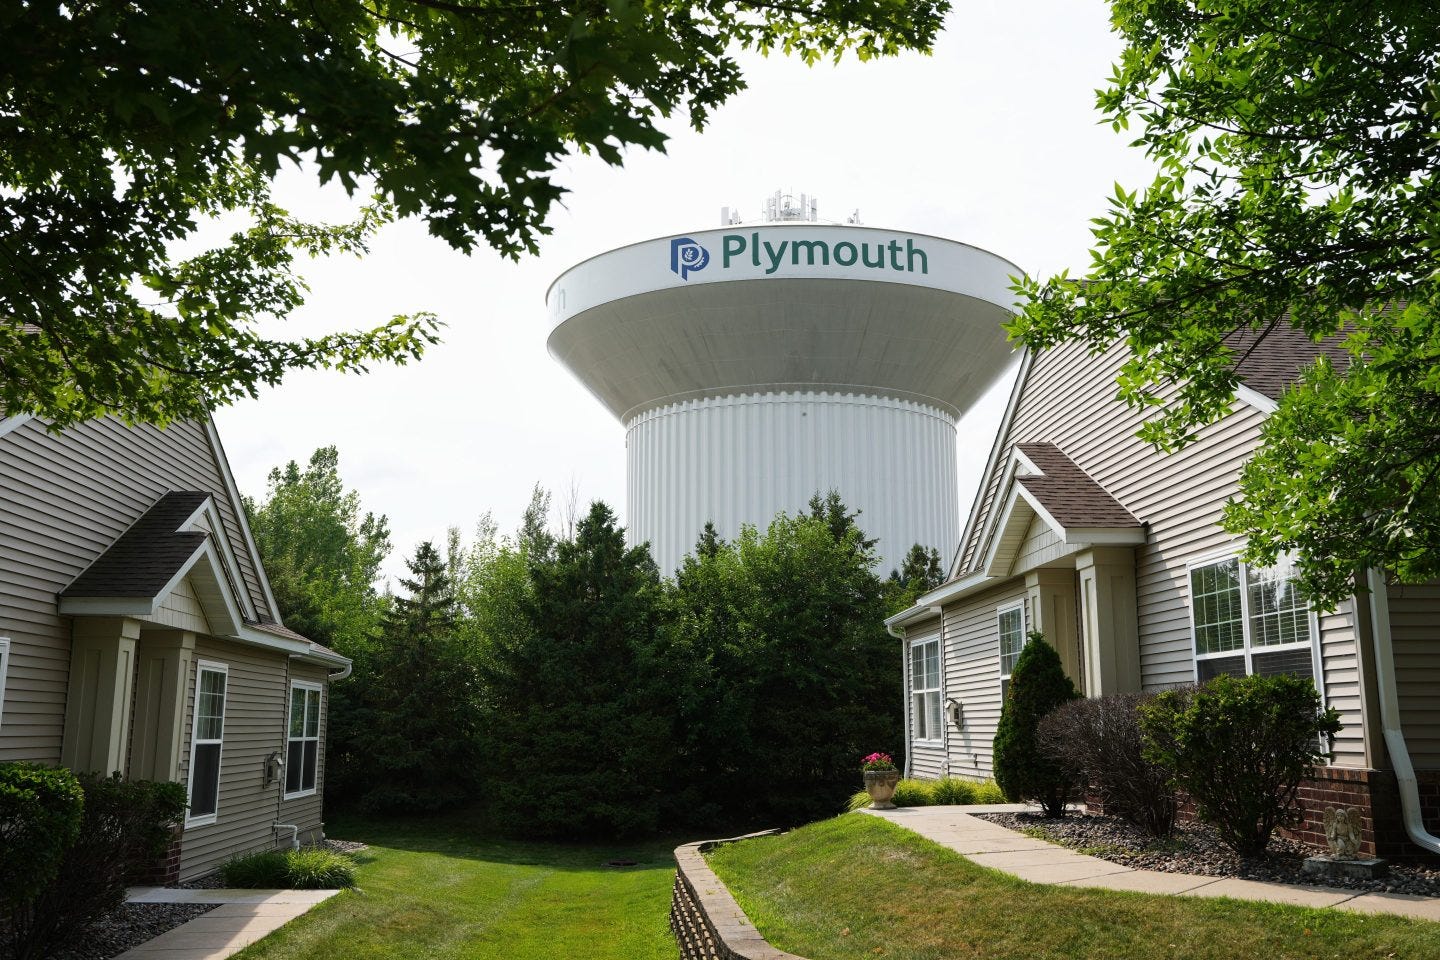
The first public sign of trouble came from Minnesota. State IT officials reported that hackers had targeted operational technology at more than thirty water systems, including the town of Plymouth, over the weekend of July 26–27.
A water tower photographed against the summer sky became the visual shorthand for a story that, underneath the calm surface, was anything but routine.
By July 30, the scope had widened. The FBI and EPA issued a stark public warning that "malicious cyber actors" were targeting programmable logic controllers, or PLCs — the devices that adjust water pressure, control chemical dosing, and keep treatment plants running within safe parameters.
Michigan confirmed nine of its own water systems had been hit. Officials there said all systems continued operating safely, but acknowledged the intrusion.
Reporting soon indicated at least five more states, not yet named publicly, had also been affected — bringing the total to seven or more.
The technical details, once they emerged, were unsettling in their simplicity. Investigators found that attackers accessed PLCs and, in some cases, remotely changed their passwords — locking legitimate operators out of the very systems meant to keep drinking water safe.
The stated goal, according to officials briefed on the intrusions, was to cause a loss of system pressure and create the potential for water contamination. No contamination was ultimately reported. But several utilities issued boil-water notices out of caution, and some experienced actual pressure loss and flooding as operators scrambled to regain control.
Acting CISA Director Nick Anderson described the scale of the exposure in blunt terms, saying the agency was tracking a significant rise in actors going after PLCs at water utilities nationwide, and urged operators to pull exposed equipment off the public internet immediately.
What makes this episode different from a routine cybercrime wave is what didn't happen. There was no ransom demand, no extortion attempt, no dark-web leak site threatening to publish stolen data unless a utility paid up.
Security analysts have called this one of the most serious cyberattacks on U.S. water systems in years — not because of the damage it caused, which was contained, but because of what its restraint implied about the attacker's intent.
II. The Vulnerability Nobody Patched
To understand why this kept happening — and why it will likely happen again — you have to look past the headlines about Minnesota and Michigan and into the guts of the equipment itself.
At the center of this story is a specific flaw: CVE-2021-22681, a critical authentication bypass affecting Rockwell Automation's Logix line of industrial controllers. It carries a severity score of 9.8 out of 10 — about as serious as vulnerabilities get. It has no vendor patch. It was first disclosed years ago, and it sat there, known and unfixed, until March 2026, when CISA added it to its Known Exploited Vulnerabilities catalog after confirming Iranian-affiliated actors were actively using it in the wild.
That's worth sitting with. This wasn't a zero-day, a surprise flaw nobody could have anticipated. It was a known hole in the fence, left open for years, in equipment running some of the country's most essential infrastructure.
And the fence, it turns out, has a lot more holes than most people would expect.
Internet-scanning research conducted by the cybersecurity firm Tenable identified more than five thousand internet-exposed hosts worldwide that responded to industrial protocols and identified themselves as Rockwell Automation or Allen-Bradley devices.
The United States accounted for nearly three-quarters of that global exposure — roughly 3,891 hosts. A disproportionate number of them connect over cellular carrier networks, meaning they're field-deployed devices reachable essentially the same way a cell phone is reachable: directly, from anywhere, without needing to breach a corporate network first.
That cellular exposure is precisely the vector investigators believe was used in the Plymouth, Minnesota breach.
The EPA has separately estimated that more than seventy percent of U.S. water systems inspected have some kind of cybersecurity deficiency.
Put those numbers together and the picture is less "sophisticated nation-state operation" and more "unlocked doors, at scale, discovered by someone who went looking." That doesn't make the threat less serious — arguably it makes it more so, because it means the barrier to entry for the next attacker, whoever they are, is not very high.
Federal advisories updated on July 22 — just days before the Minnesota attacks began — expanded the list of known-targeted manufacturers beyond Rockwell to include Schneider Electric and Siemens equipment as well, and added new guidance for detecting a subtler form of tampering: manipulation of reusable code modules embedded inside PLC programs, rather than just obvious changes to control settings. That detail matters, because it suggests investigators had already seen attackers hiding their changes inside code that operators wouldn't think to inspect.
III. The Paper Trail
The federal warnings did not start in July. They trace back further, and the trail itself tells a story about a threat that was seen coming.
The foundational advisory — "Iranian-Affiliated Cyber Actors Exploit Programmable Logic Controllers (PLCs) Across U.S. Critical Infrastructure" — was first published in April 2026 by CISA, the FBI, EPA, and NSA jointly. It warned that Iranian-affiliated actors were targeting internet-connected operational technology with the apparent intent of causing disruption, including tampering with project files and manipulating the displays operators use to monitor plant conditions in real time.
EPA Assistant Administrator for Water Jess Kramer framed the stakes plainly at the time, saying that cybersecurity threats pose a serious and legitimate risk to communities, hospitals, schools, and other essential services that depend on safe water systems.
FBI Cyber Division Assistant Director Brett Leatherman said the advisory was meant to help organizations defend themselves against Iran-affiliated actors, and described the effort as part of imposing costs on those responsible under the administration's broader cyber strategy.
The advisory wasn't a one-time notice. It was updated on July 22, 2026 — expanding the list of targeted equipment manufacturers and adding detection guidance for the code-module tampering technique described above. Four days later, the Minnesota attacks began.
That sequence — a federal warning naming Iran-affiliated PLC exploitation, expanded and reissued days before a real-world incident matching its exact description — is the strongest circumstantial thread connecting the July attacks to Iran. It is not proof. But it is not nothing, either.
IV. Who Did This? The Case for Caution
Here's where the story resists a clean headline.
CNN reported that U.S. and state officials are treating Iran as one of the leading suspects but have explicitly not made a formal determination, and are wary of the possibility of a false flag — an operation designed by one actor to look like the work of another. Minnesota state investigators said they had identified similarities in timing and the type of technology affected across incidents, but had not yet confirmed that every attack was carried out by the same group, let alone the same nation.
CBS News, in a timeline of Iranian cyber activity against the U.S., noted that official confirmation of attribution can take weeks or months as investigators collect and verify technical evidence — a reminder that the absence of a confirmed answer isn't evidence of nothing, it's simply how this kind of investigation works.
The historical pattern lends the Iran theory real weight, even without formal confirmation. In 2023, federal agencies confirmed that actors affiliated with Iran's Islamic Revolutionary Guard Corps used a strikingly similar playbook — accessing water and wastewater facilities by exploiting internet-connected controllers, in that case Israeli-made Unitronics devices, left with their factory-default passwords still active. The tradecraft in July 2026 — targeting exposed PLCs, aiming for operational disruption rather than data theft or profit — fits the same signature.
There's also a geopolitical backdrop that can't be separated from the technical analysis. Iranian-affiliated targeting of U.S. critical infrastructure escalated sharply following the 2026 Iran war between the U.S., Israel, and Iran. And the infrastructure-attack narrative runs in both directions. In March 2026, in the opening days of that conflict, Iran accused the United States of striking a freshwater desalination plant on Qeshm Island in the Strait of Hormuz, disrupting water supplies to roughly thirty villages. Iranian Foreign Minister Abbas Araghchi called it a "blatant and desperate crime," and argued that the U.S. had set the precedent for targeting water infrastructure, not Iran. The United States and Israel both denied conducting that strike.
Whether or not that denial holds up, the accusation itself matters for understanding the current moment: both nations now have a public narrative in which the other is accused of weaponizing water infrastructure against civilians. That doesn't make either claim untrue. But it's a reminder that attribution in cyberspace — and in war more broadly — is never just a technical exercise. It's also a political one, made in an environment where both sides have reasons to shape the story.
V. A President at Odds With His Own Agencies
While EPA, FBI, CISA, and NSA officials were describing an urgent, ongoing, Iran-affiliated threat to the nation's water infrastructure, President Trump was telling a different story.
At a cabinet meeting held July 31 at Camp David, Trump blamed Minnesota state authorities — naming Democratic Governor Tim Walz specifically — for the cyberattacks, rather than Iran. "Iran should be so lucky," he said, adding that Iran had "bigger problems than worrying about Minnesota."
That framing puts the president directly at odds with the joint advisory language his own administration's agencies had just reissued days earlier — language that named Iran-affiliated actors as the threat, expanded the list of vulnerable equipment, and urged utilities nationwide to take emergency defensive action. It's a striking split: the agencies responsible for identifying and defending against the threat describe it as foreign and urgent; the president describes it as a state-level failure and dismisses the foreign angle as implausible.
This isn't a story about litigating who's right on the merits — attribution, as covered above, genuinely hasn't been formally confirmed by investigators. But the dissonance itself is newsworthy. When the federal government's technical agencies and its chief executive are telling the public two different stories about the same active national security threat, the public is left to sort out not just what happened to their water supply, but who to believe about it.
VI. What Comes Next
Regardless of how attribution eventually shakes out, the fixes CISA and EPA are recommending don't wait on that answer. Updated guidance urges water utilities to:
Remove PLCs and other operational technology from direct internet exposure
Place any necessary remote access behind a secure gateway and firewall
Change all default manufacturer passwords immediately
Monitor PLC project files for unauthorized changes, including tampering with reusable code modules
Inform third-party service providers of active threats to connected devices
Consider isolated network architectures that separate OT systems from the broader internet entirely
None of this is exotic advice. Much of it amounts to basic digital hygiene that a well-resourced municipal utility should already have in place. That it still needs to be said, in 2026, after a nearly identical style of attack in 2023, is itself part of the story.
What's clear is that this is now a pattern, not an isolated event: 2023's Unitronics campaign, the April 2026 advisory, the July 22 update, and the attacks that followed days later. Each cycle repeats the same basic shape — exposed, unpatched, internet-connected equipment; a suspected but unconfirmed Iranian hand; and a federal warning system that keeps identifying the danger a little too late to prevent the next round.
The water reached taps safely this time. The systems that deliver it remain, by the government's own admission, exposed in ways that are well understood and have not yet been fixed.
Sources: CNN, CBS News, the Associated Press, Fortune, the Times of Israel, Cyber Magazine, HSToday, AFCEA International, the ARC Advisory Group, Tenable, the U.S. Environmental Protection Agency, and the Cybersecurity and Infrastructure Security Agency (CISA Advisory AA26-097A).